Connect an AWS Account (CloudCADI hosted on GCP)
Prerequisites
Open CloudCADI's AWS onboarding page and note down the three values shown there - Issuer, Subject, and Audience.
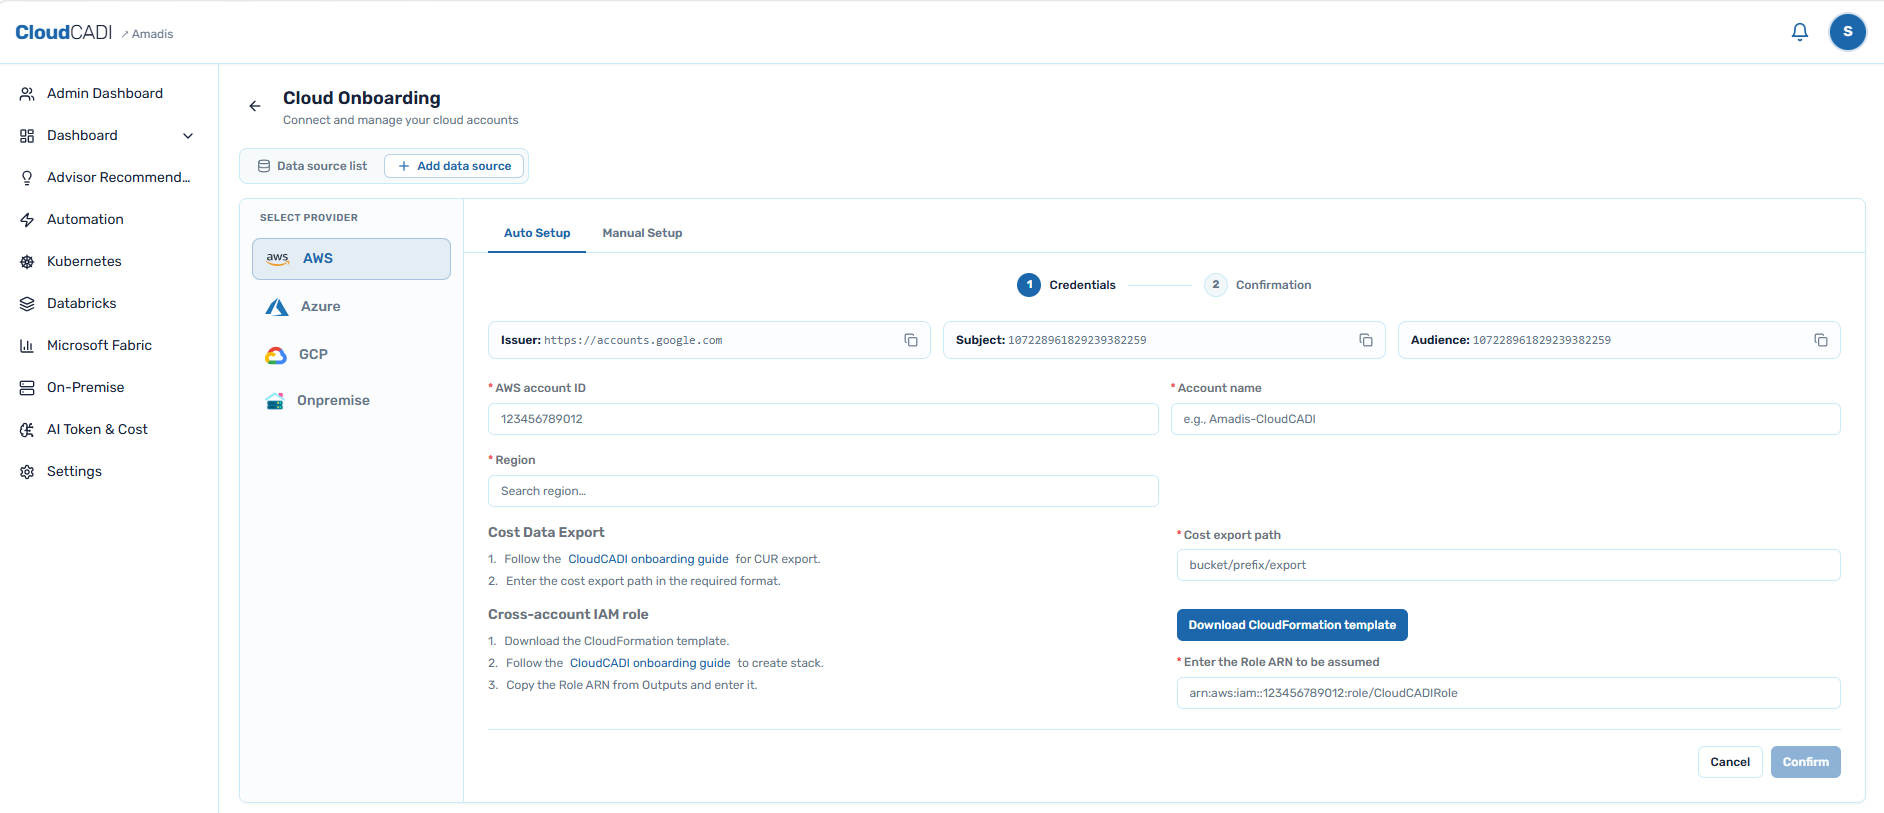
Auto Setup
First account (one-time setup):
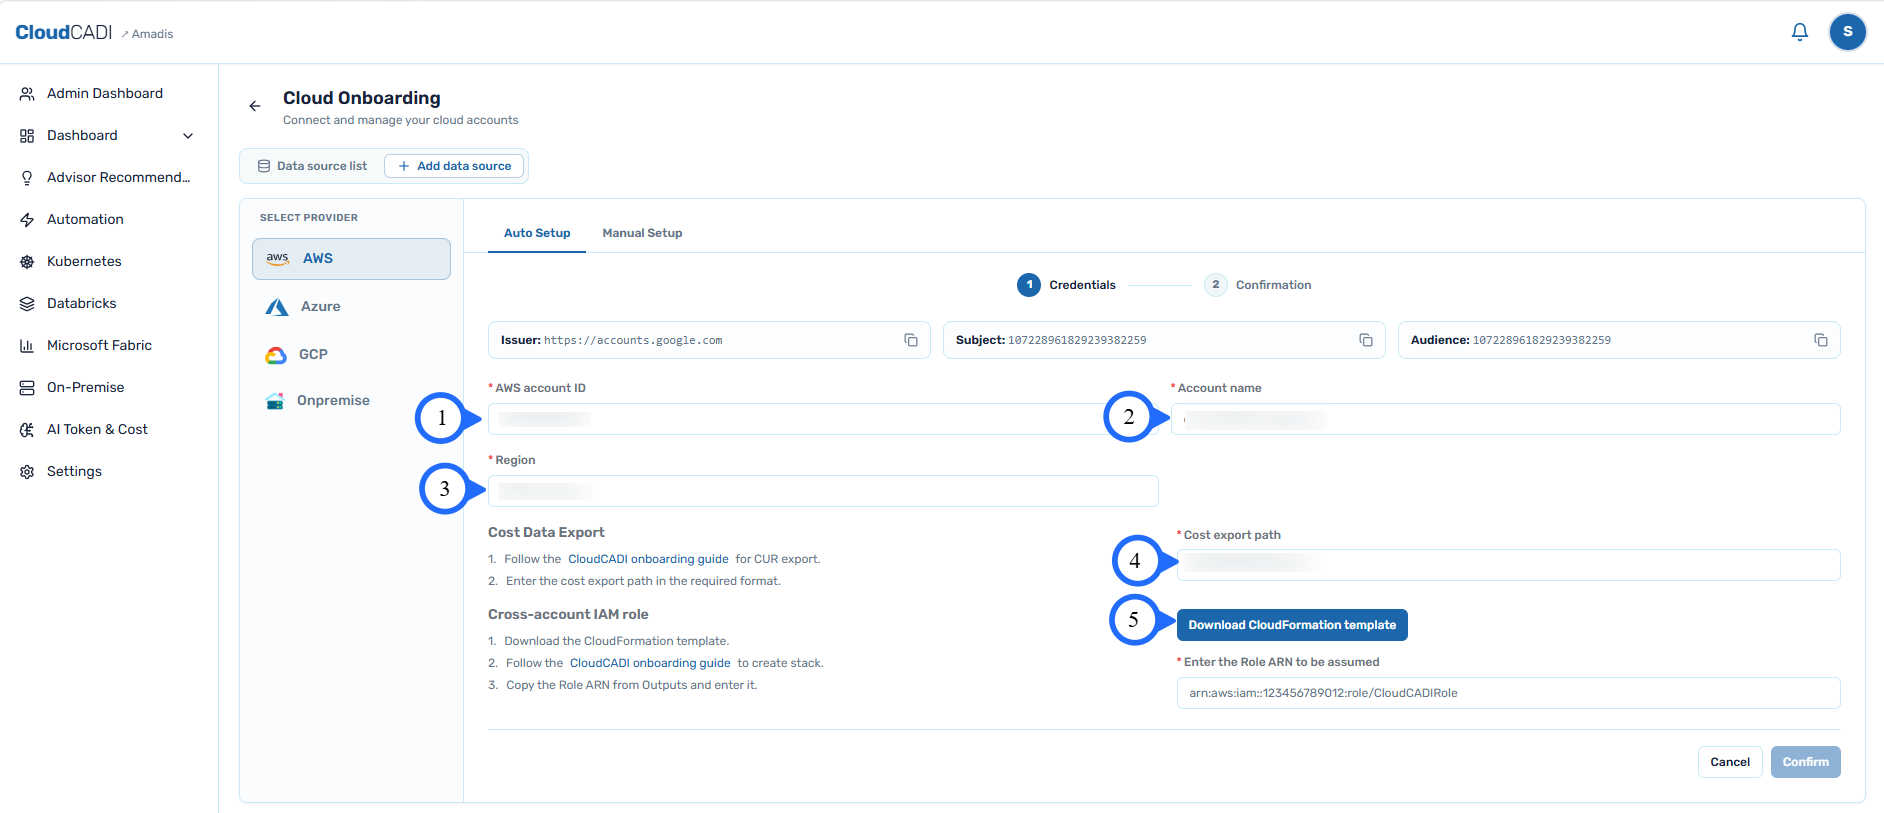
Step 1 - Enter Account Details and Download Template
-
Enter the AWS account ID, Account name, Region, and Cost export path, then download the CloudFormation template.
Step 2 - Deploy CloudFormation Stack
-
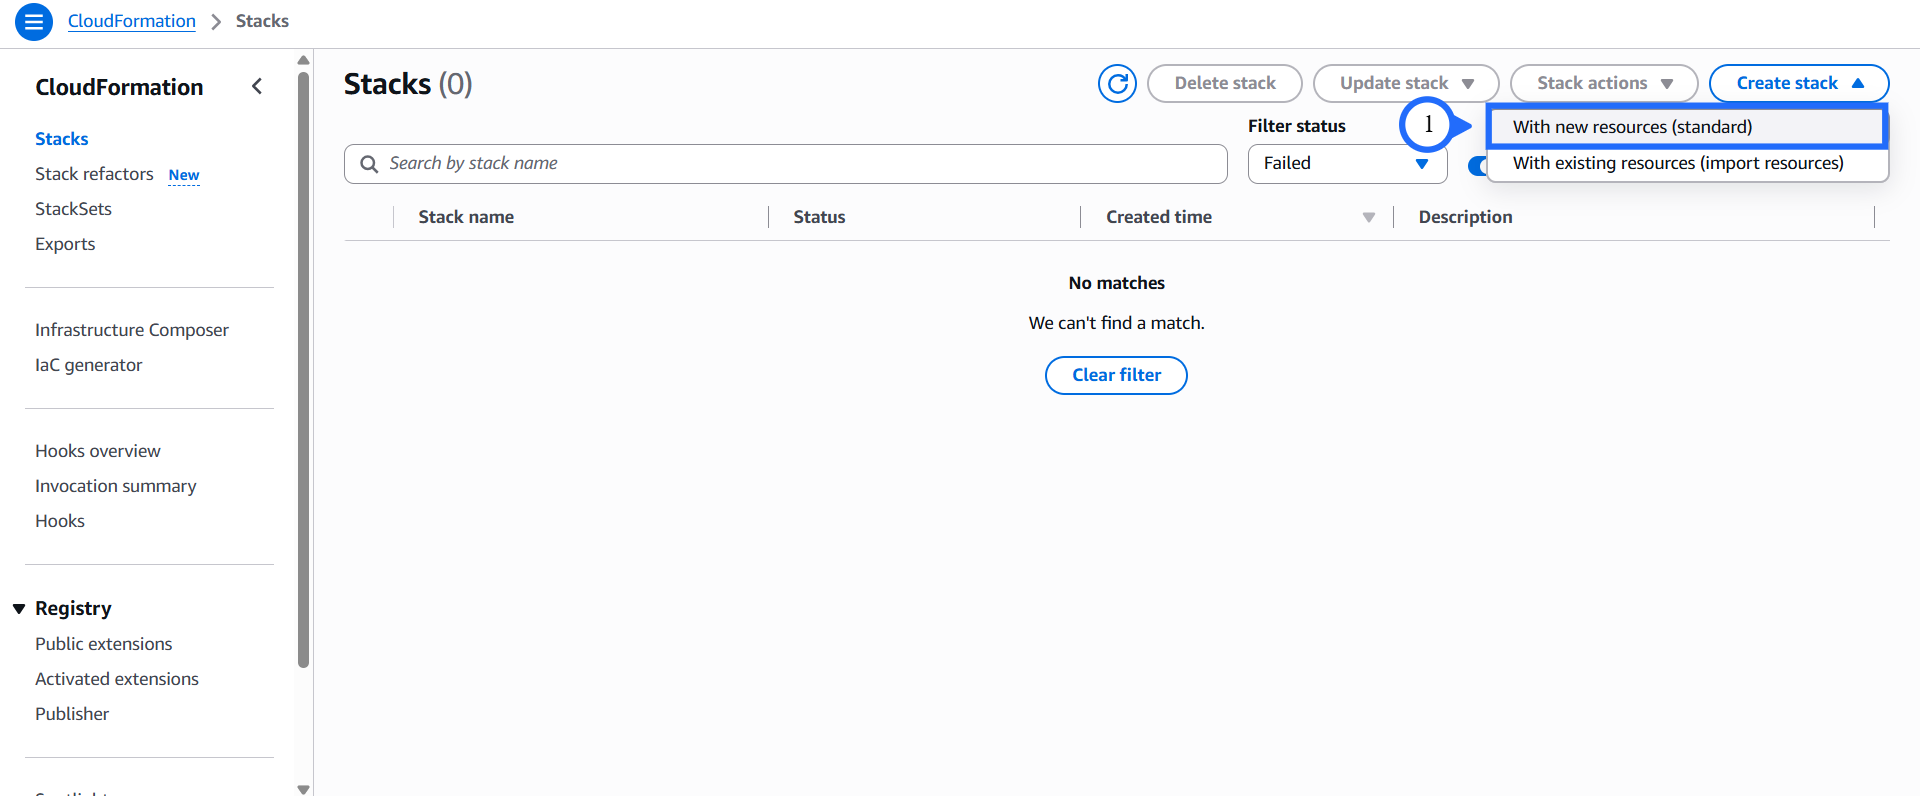
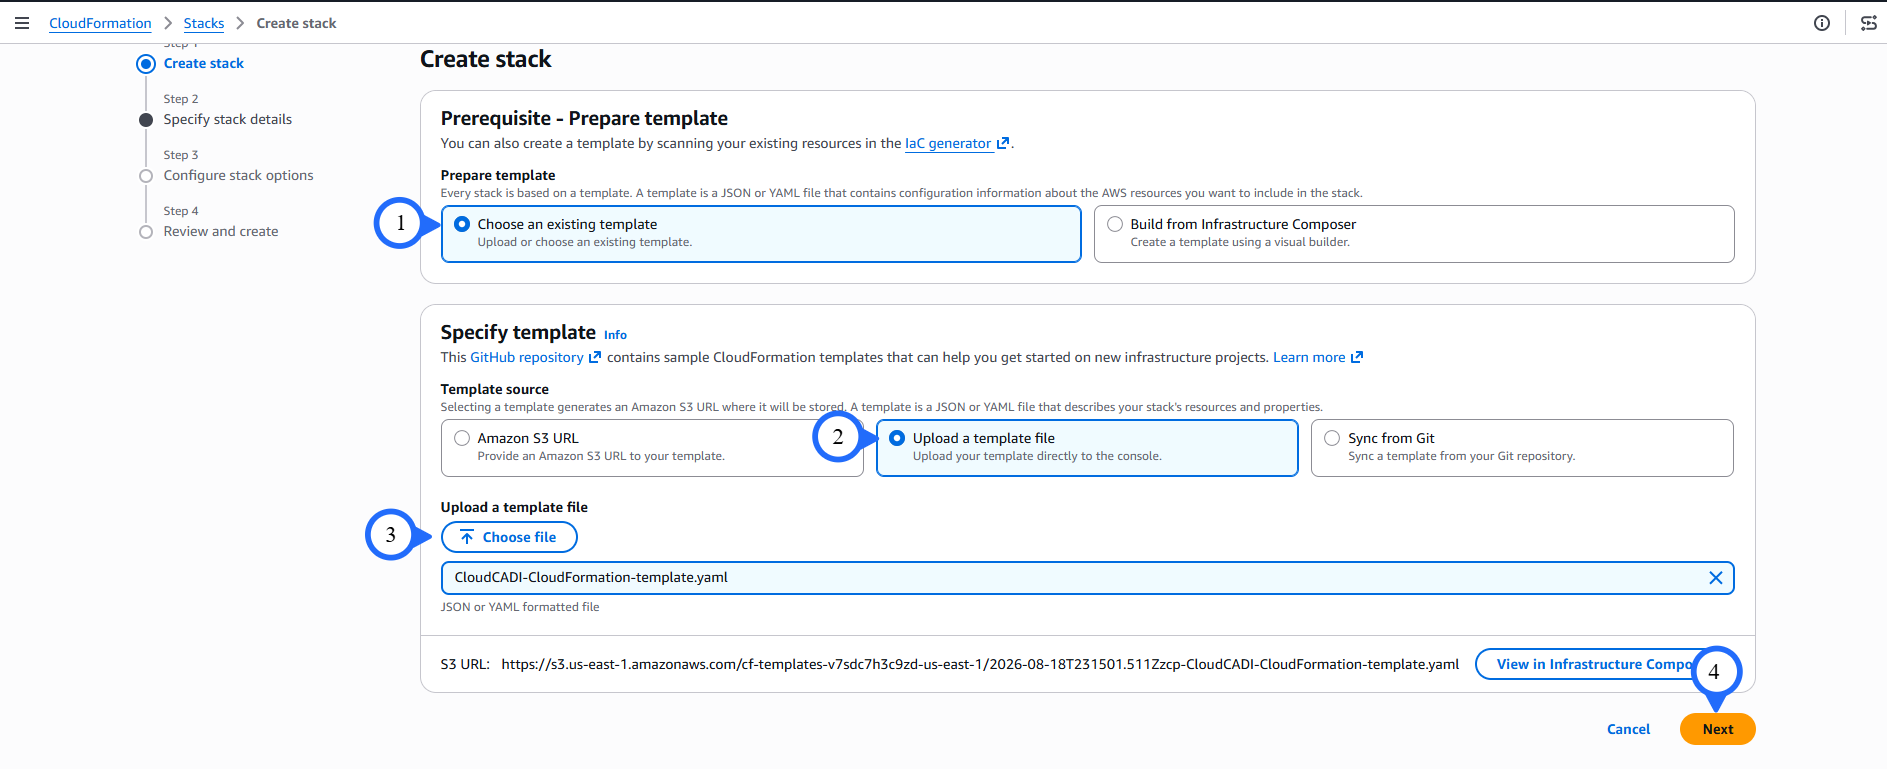
CloudFormation → Stacks → Create stack → With new resources (standard).
-
Choose an existing template → Upload a template file → Choose file → select the downloaded template → Next.
-
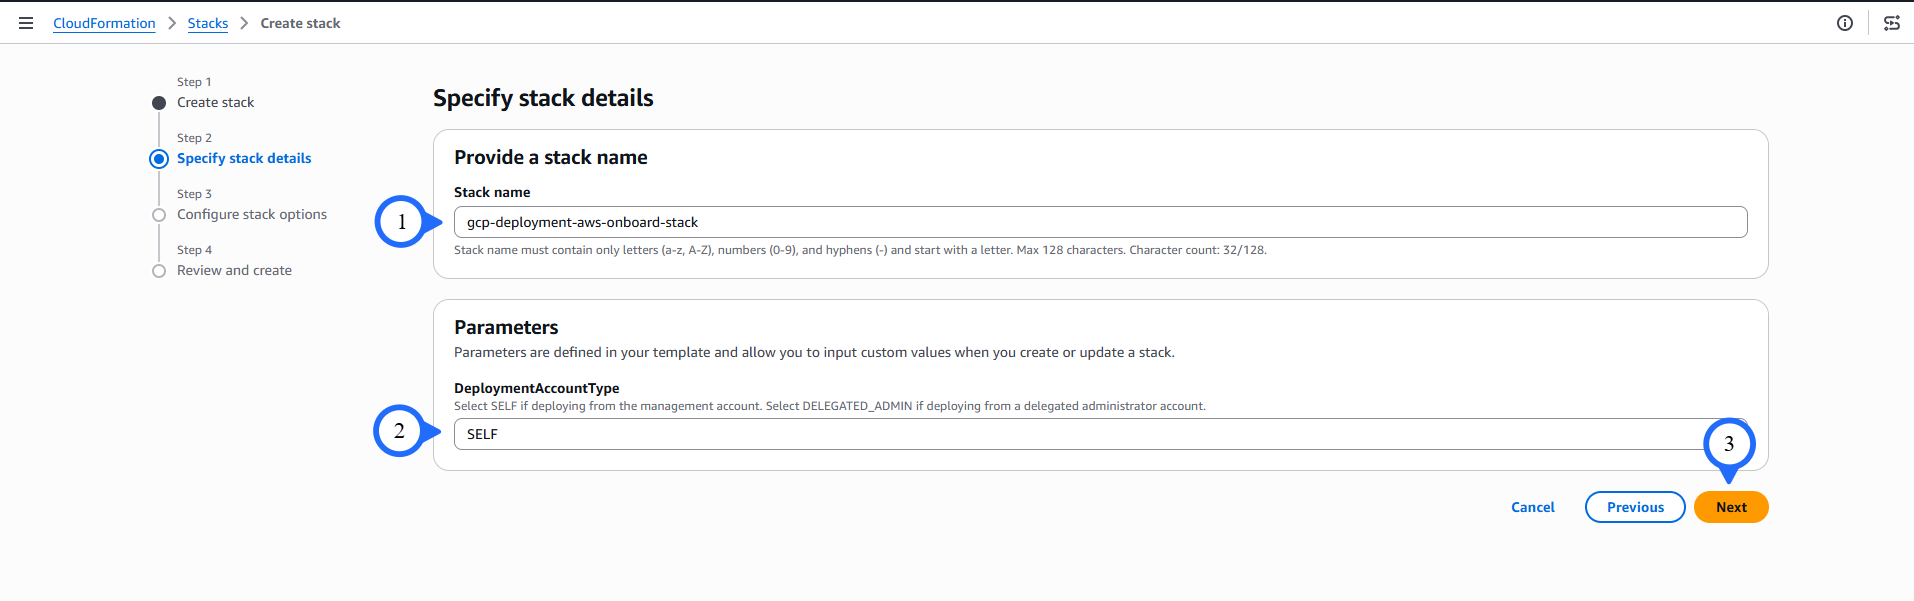
Under specify stack details. Enter stack name.
-
For DeployedAccountType, select SELF if the CloudCADI deployed account is the AWS Organizations management account. Select DELEGATED_ADMIN if it is a member account configured as a delegated administrator.
Enable Delegated Administrator
Follow these steps to enable a delegated administrator in AWS Organizations:
-
Sign in to the AWS Management Account and open AWS Organizations → Services.
-
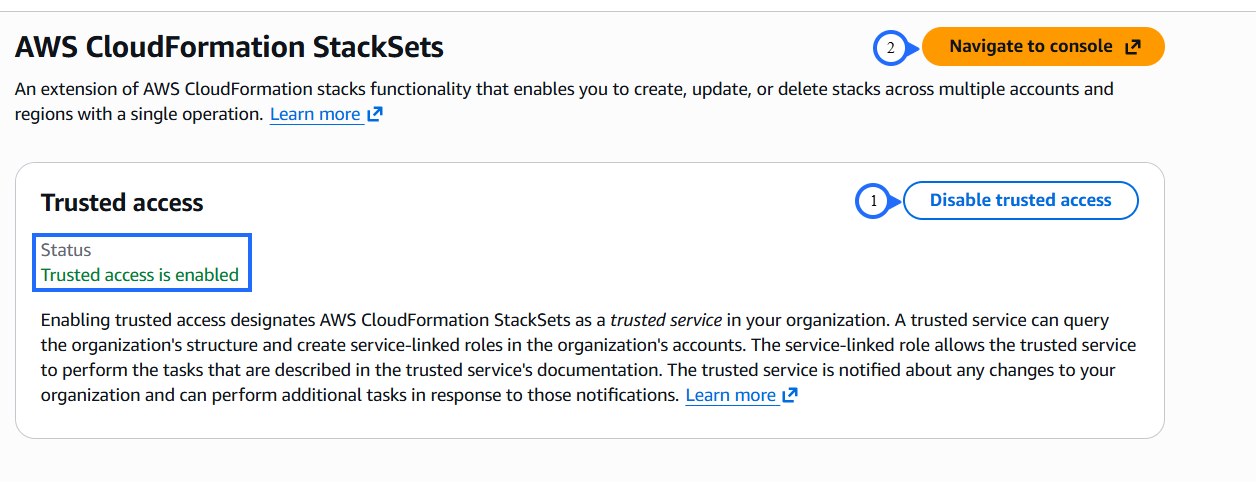
Find AWS CloudFormation StackSets and click Enable trusted access.
-
Click Navigate to Console.
-
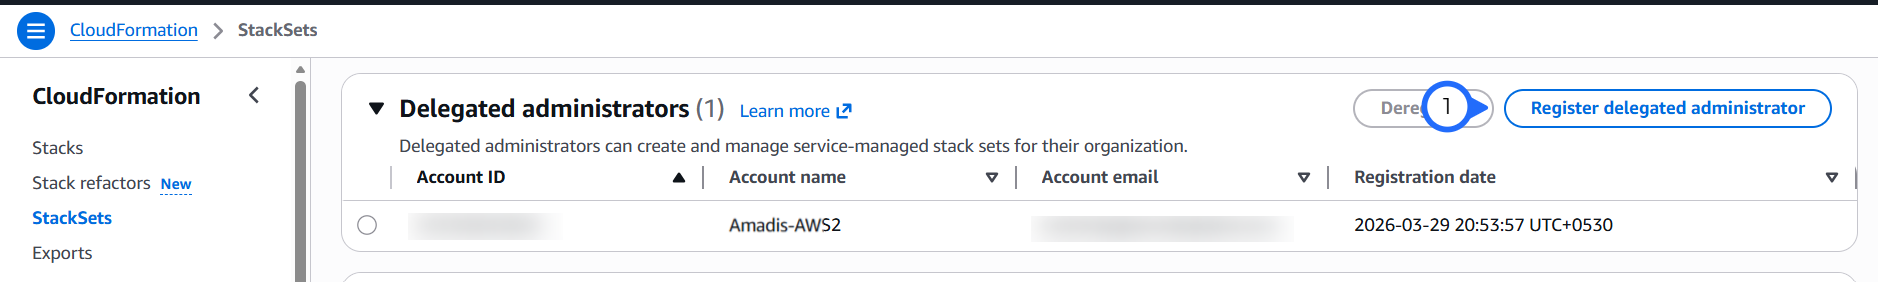
Under Delegated Administrators, click Register delegated administrator.
-
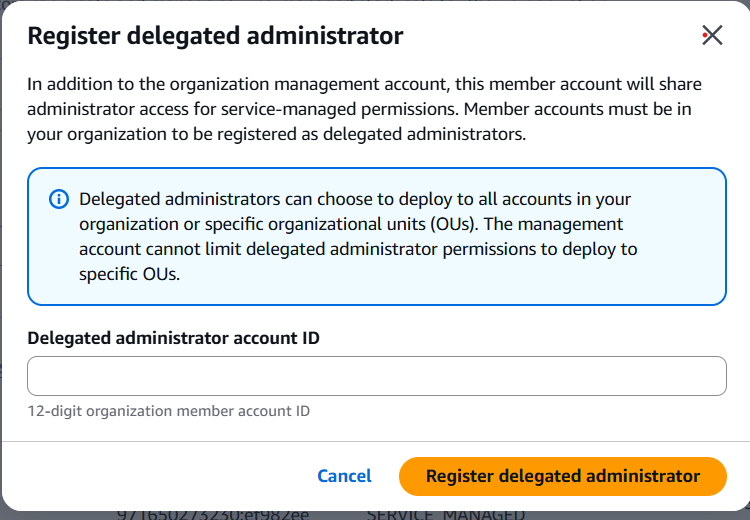
A popup will appear. Enter the Delegated Administrator Account ID and click Register Delegated Administrator.
-
The member account can now perform the required actions.
-
-
Click Next.
-
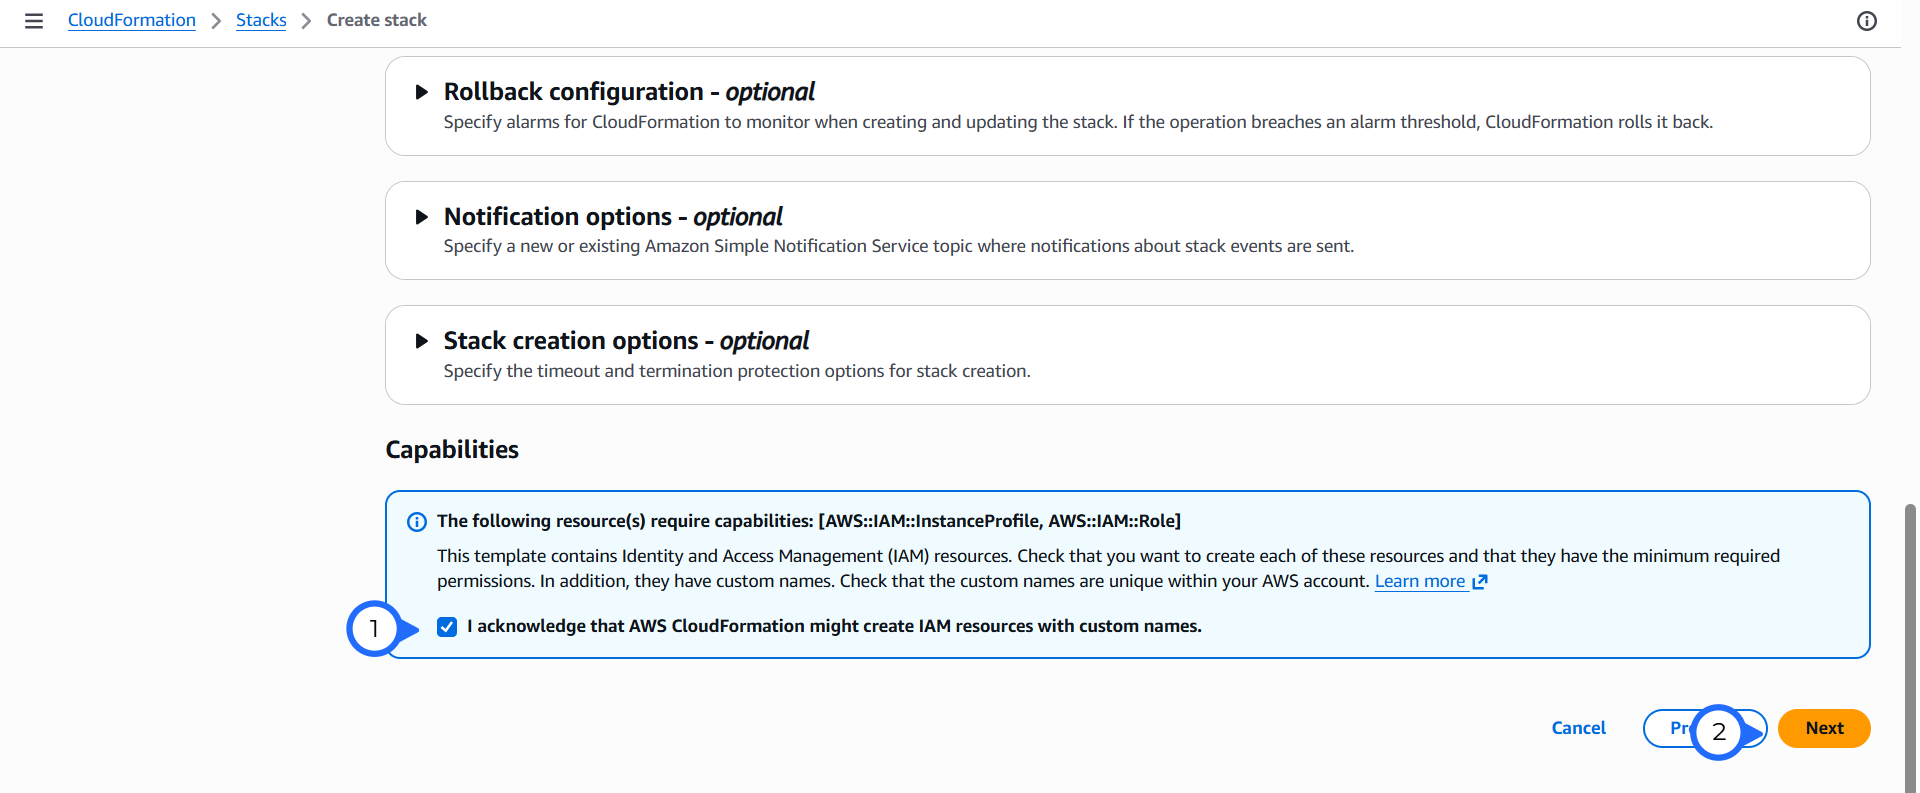
Check I acknowledge that AWS CloudFormation might create IAM resources with custom names → Next.
-
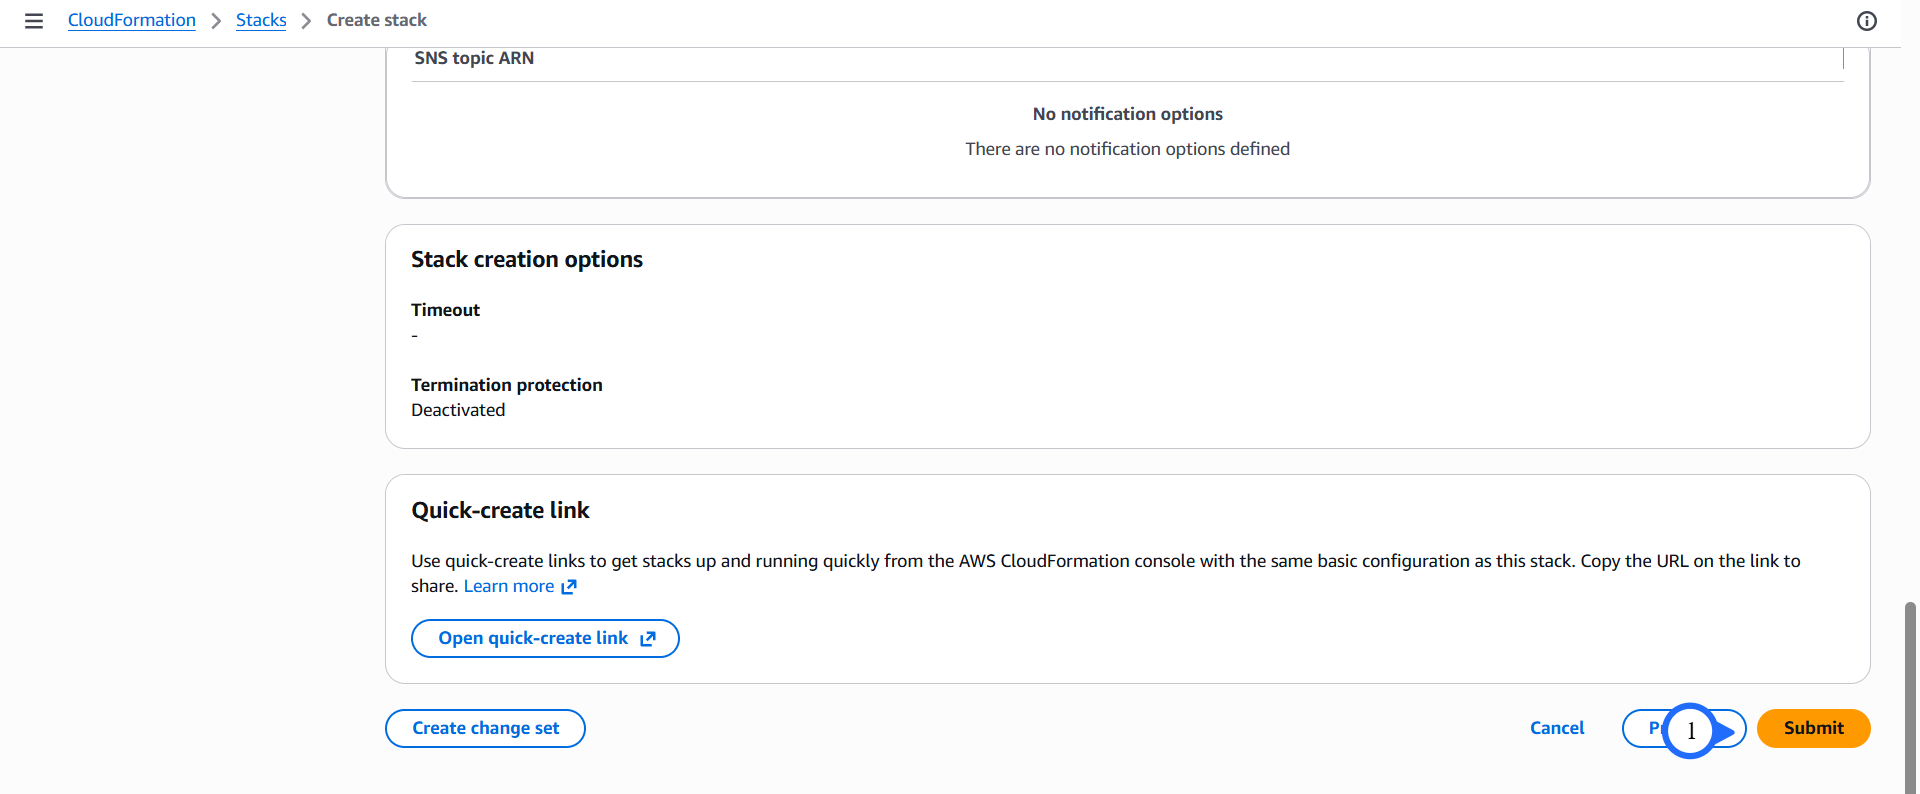
Scroll to the bottom and click Submit.
Step 3 - Complete Account Onboarding
-
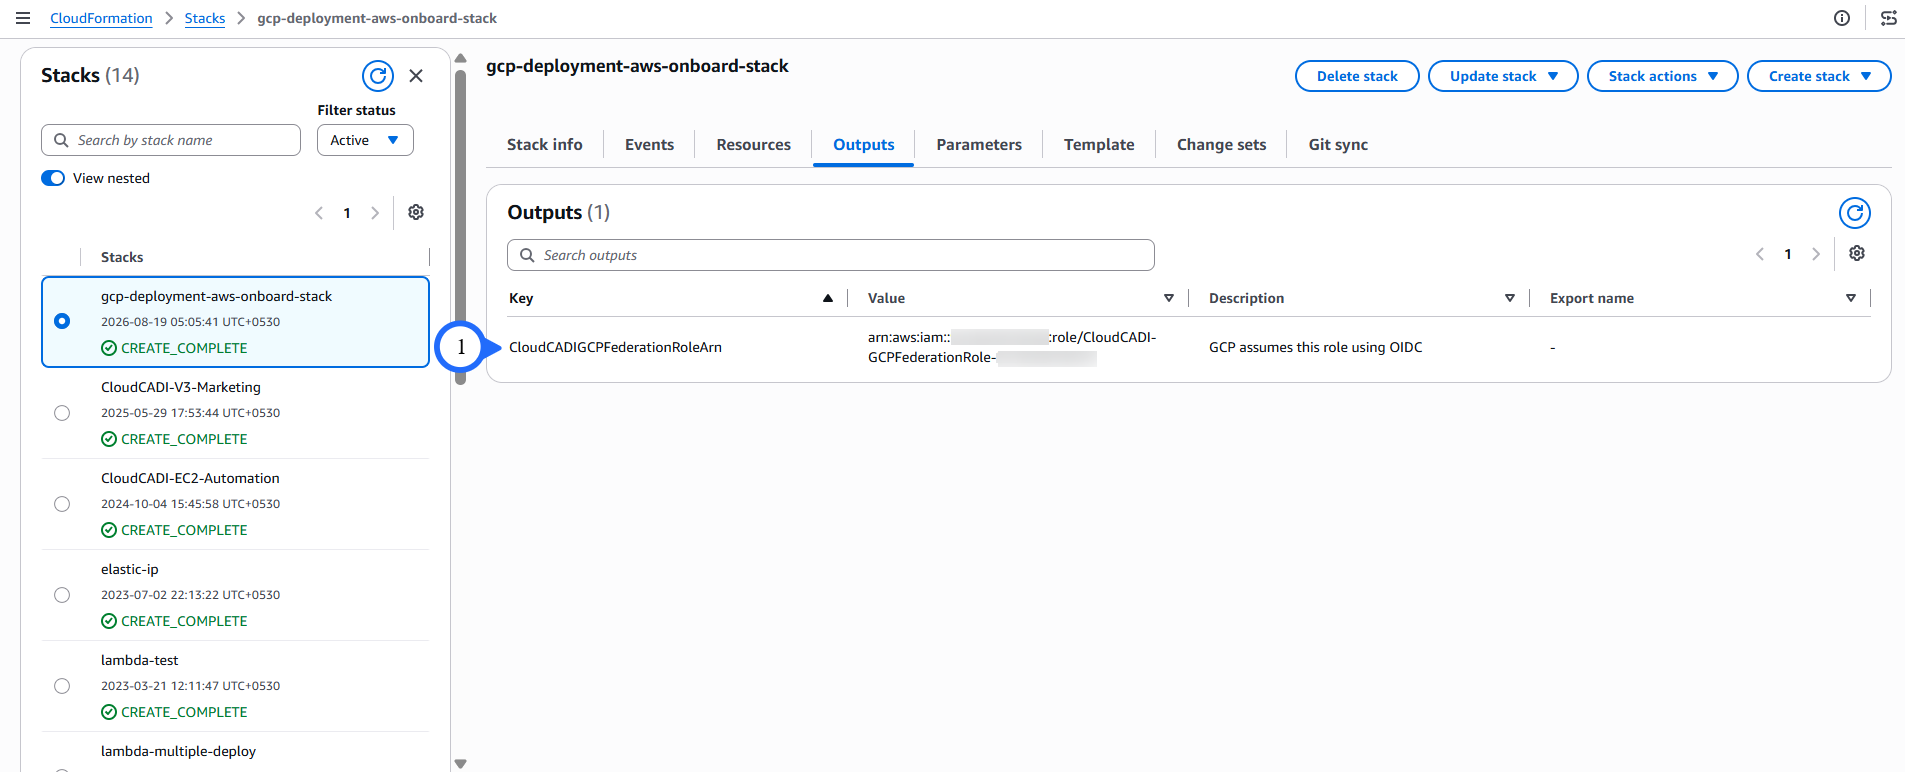
Once the stack shows CREATE_COMPLETE, copy the CloudCADIGCPFederationRoleArn from its Outputs tab, paste it into CloudCadi, and click Confirm.
-
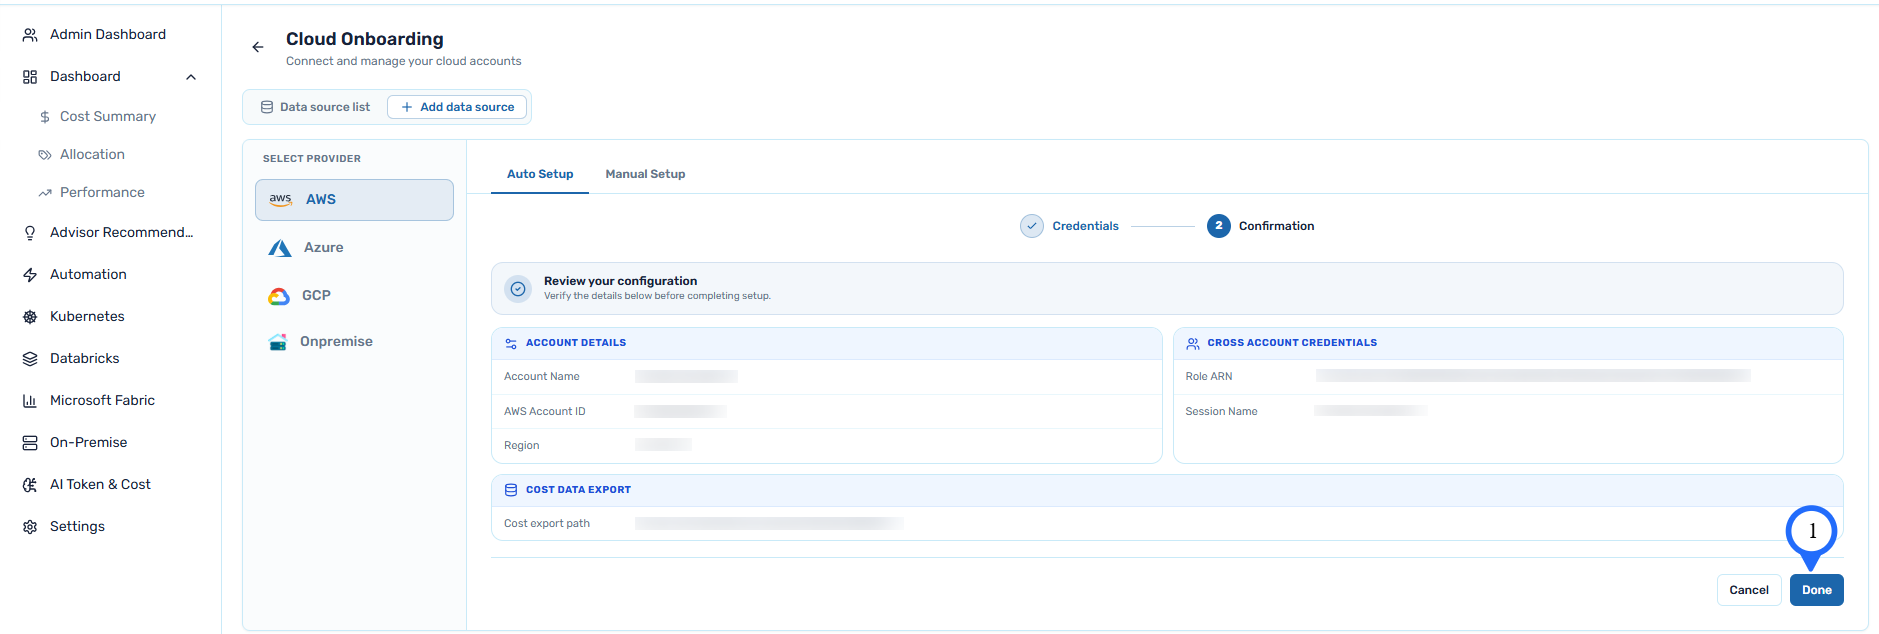
Review the configuration and click Done - this account is now onboarded.
Step 4 - Onboard Additional Accounts
-
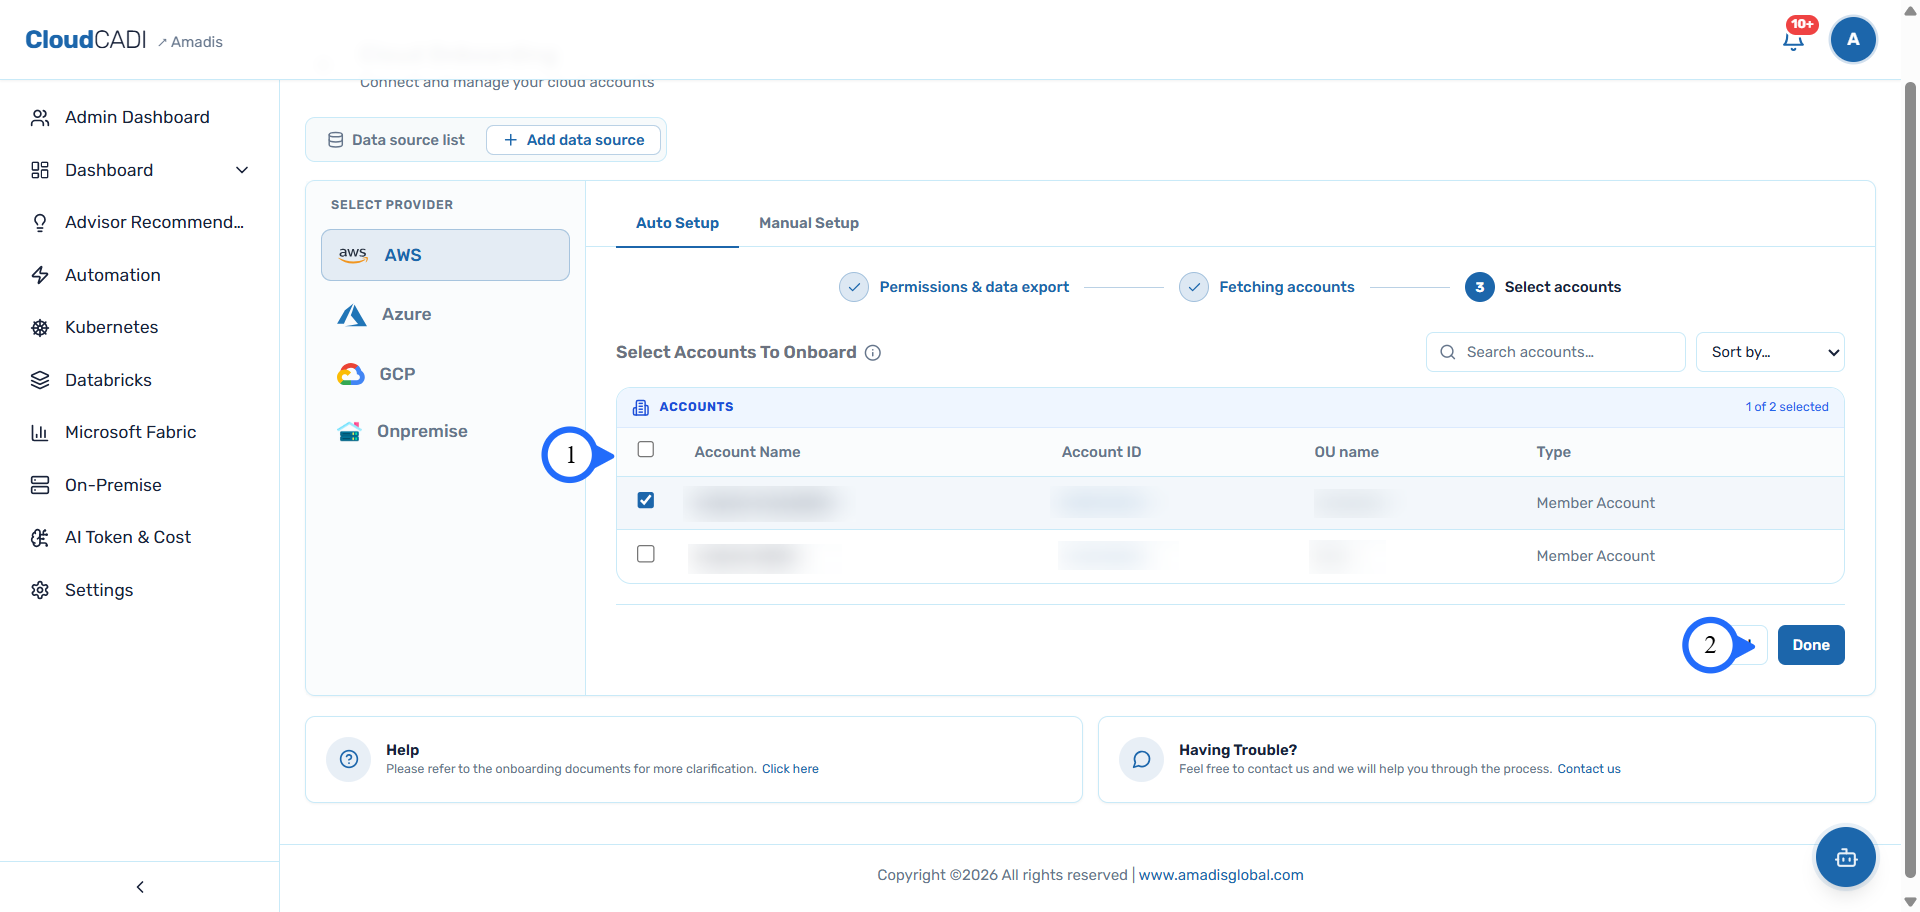
All other accounts in the same AWS Organization are fetched automatically. Select the accounts to onboard and click Done.
Manual Setup
Step 1 - Enter Account Details and Download Template
-
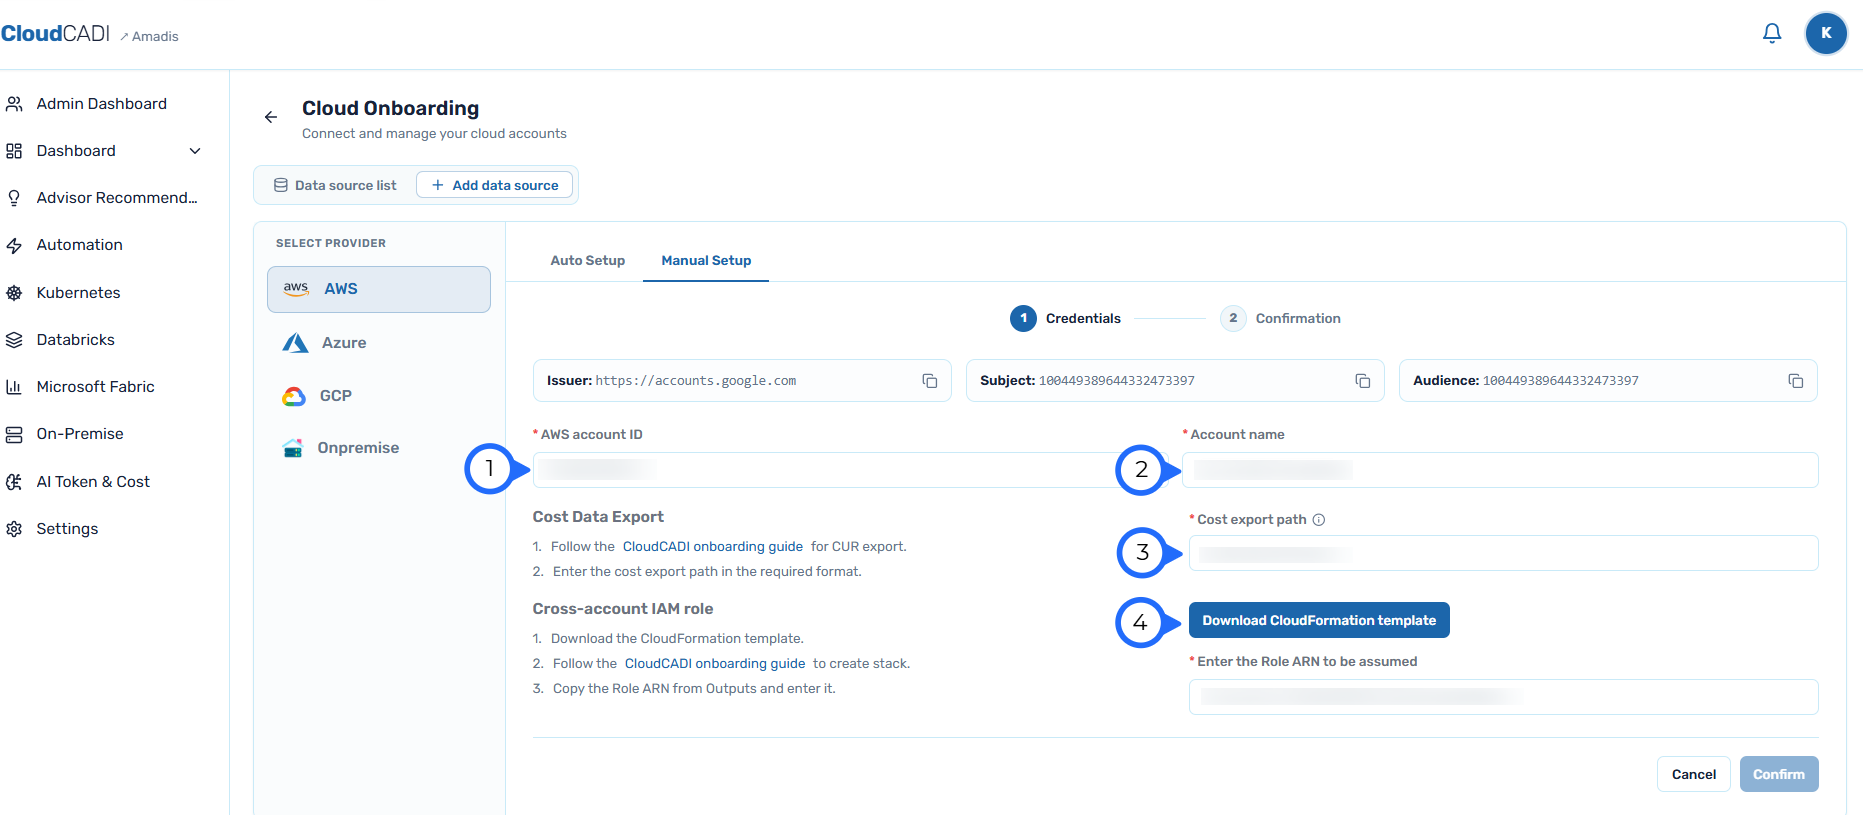
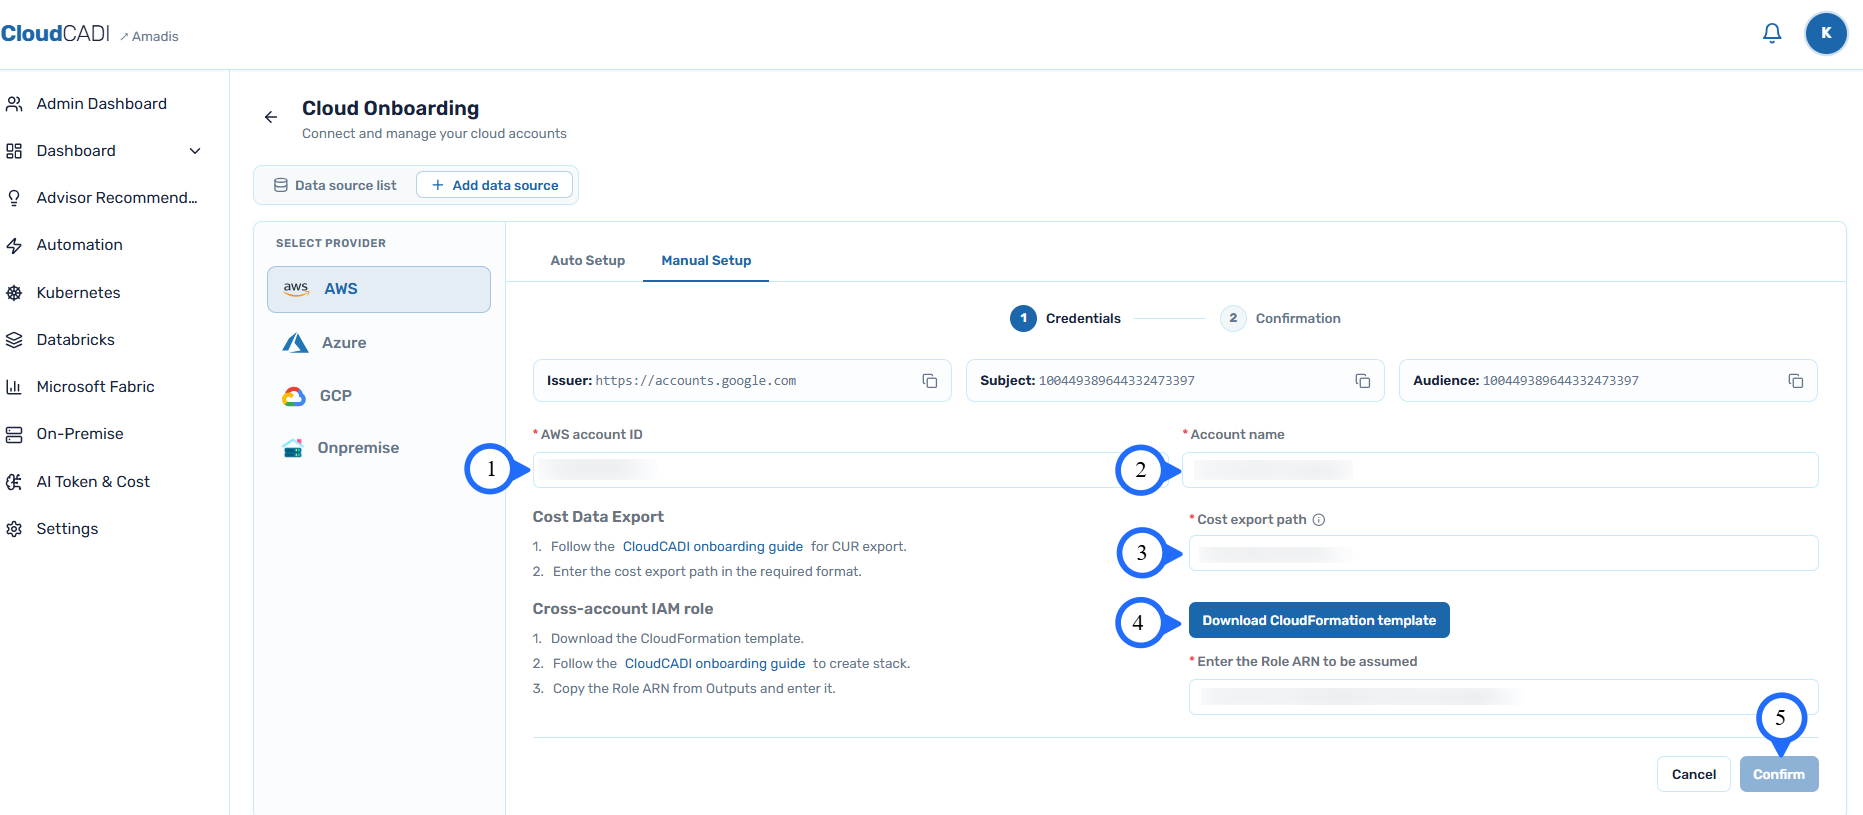
Enter the AWS account ID, Account name, and Cost export path, then download the CloudFormation template.
Step 2 - Deploy CloudFormation Stack
-
In the AWS Console, go to CloudFormation → Stacks → Create stack → With new resources (standard).
-
Under Prepare template, leave Choose an existing template selected. Under Specify template, choose Upload a template file → Choose file → select the template downloaded in step 1 → Next.
-
On Specify stack details, enter a Stack name (e.g.
gcp-aws-onboarding-stack) → Next.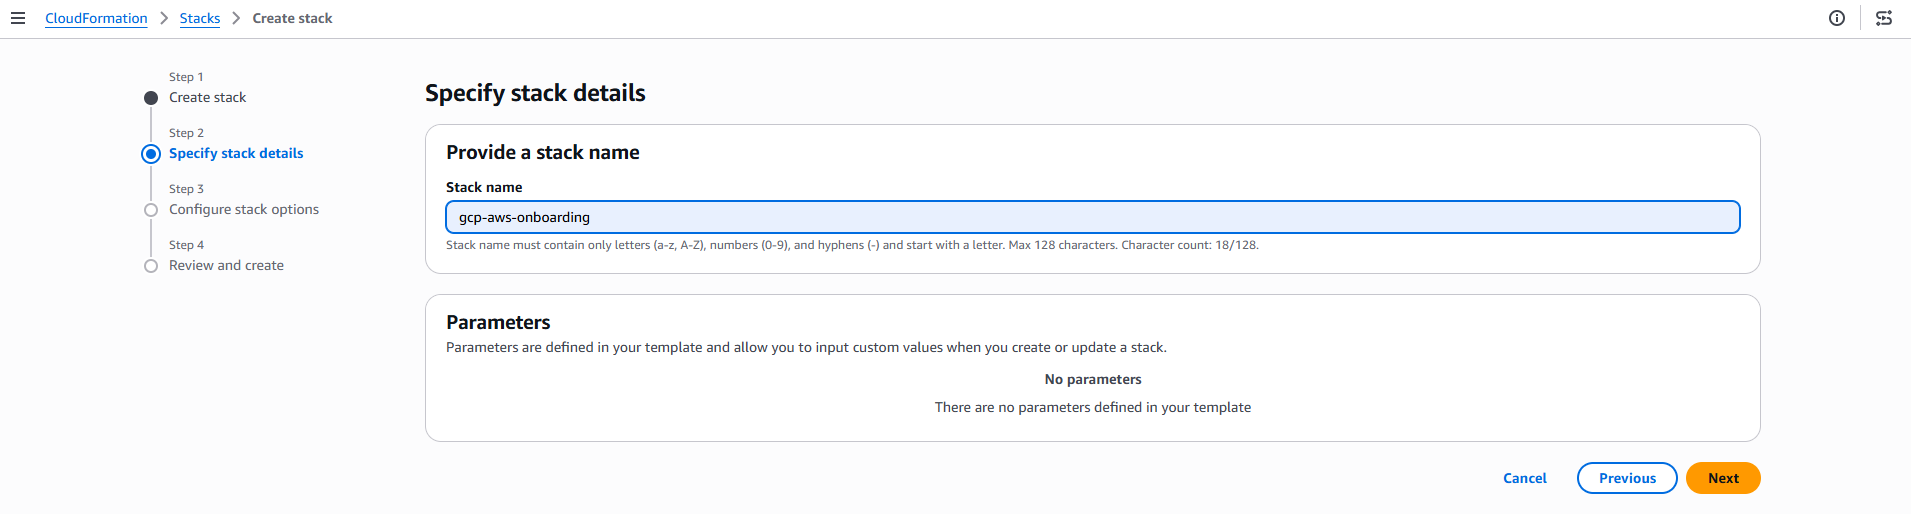
-
On Configure stack options, scroll down to Capabilities and check I acknowledge that AWS CloudFormation might create IAM resources with custom names → Next.
-
On Review and create, scroll to the bottom and click Submit.
Step 3 - Complete Account Onboarding
-
Once the stack status shows CREATE_COMPLETE, open its Outputs tab and copy the CloudCADIGCPFederationRoleArn value.
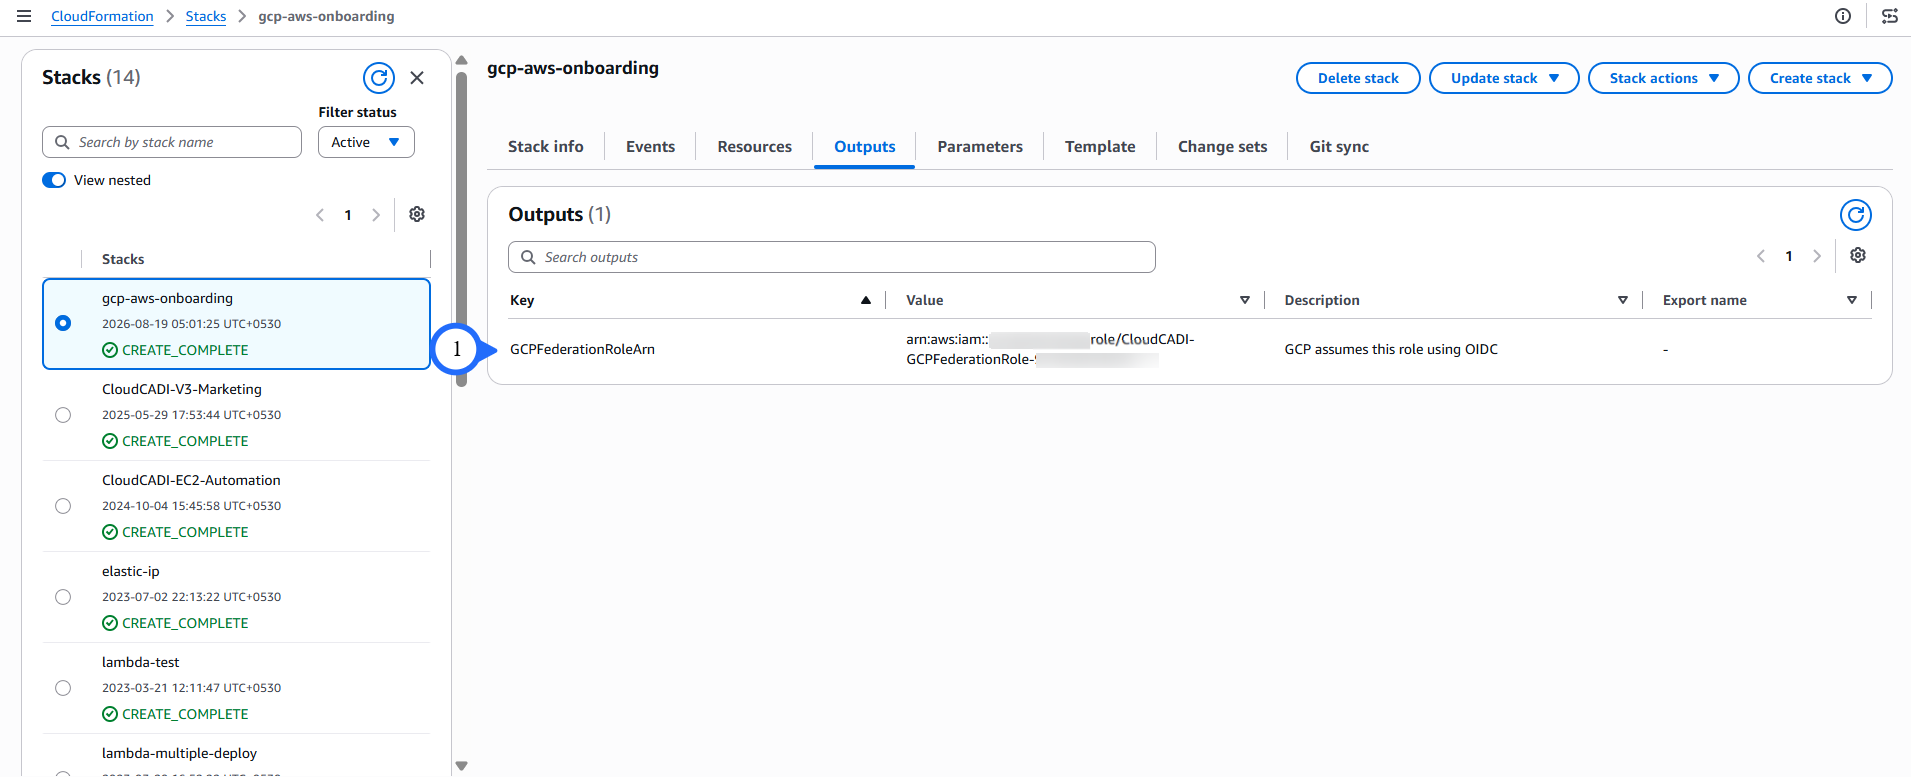
Back in CloudCadi, paste it in and click Confirm.
-
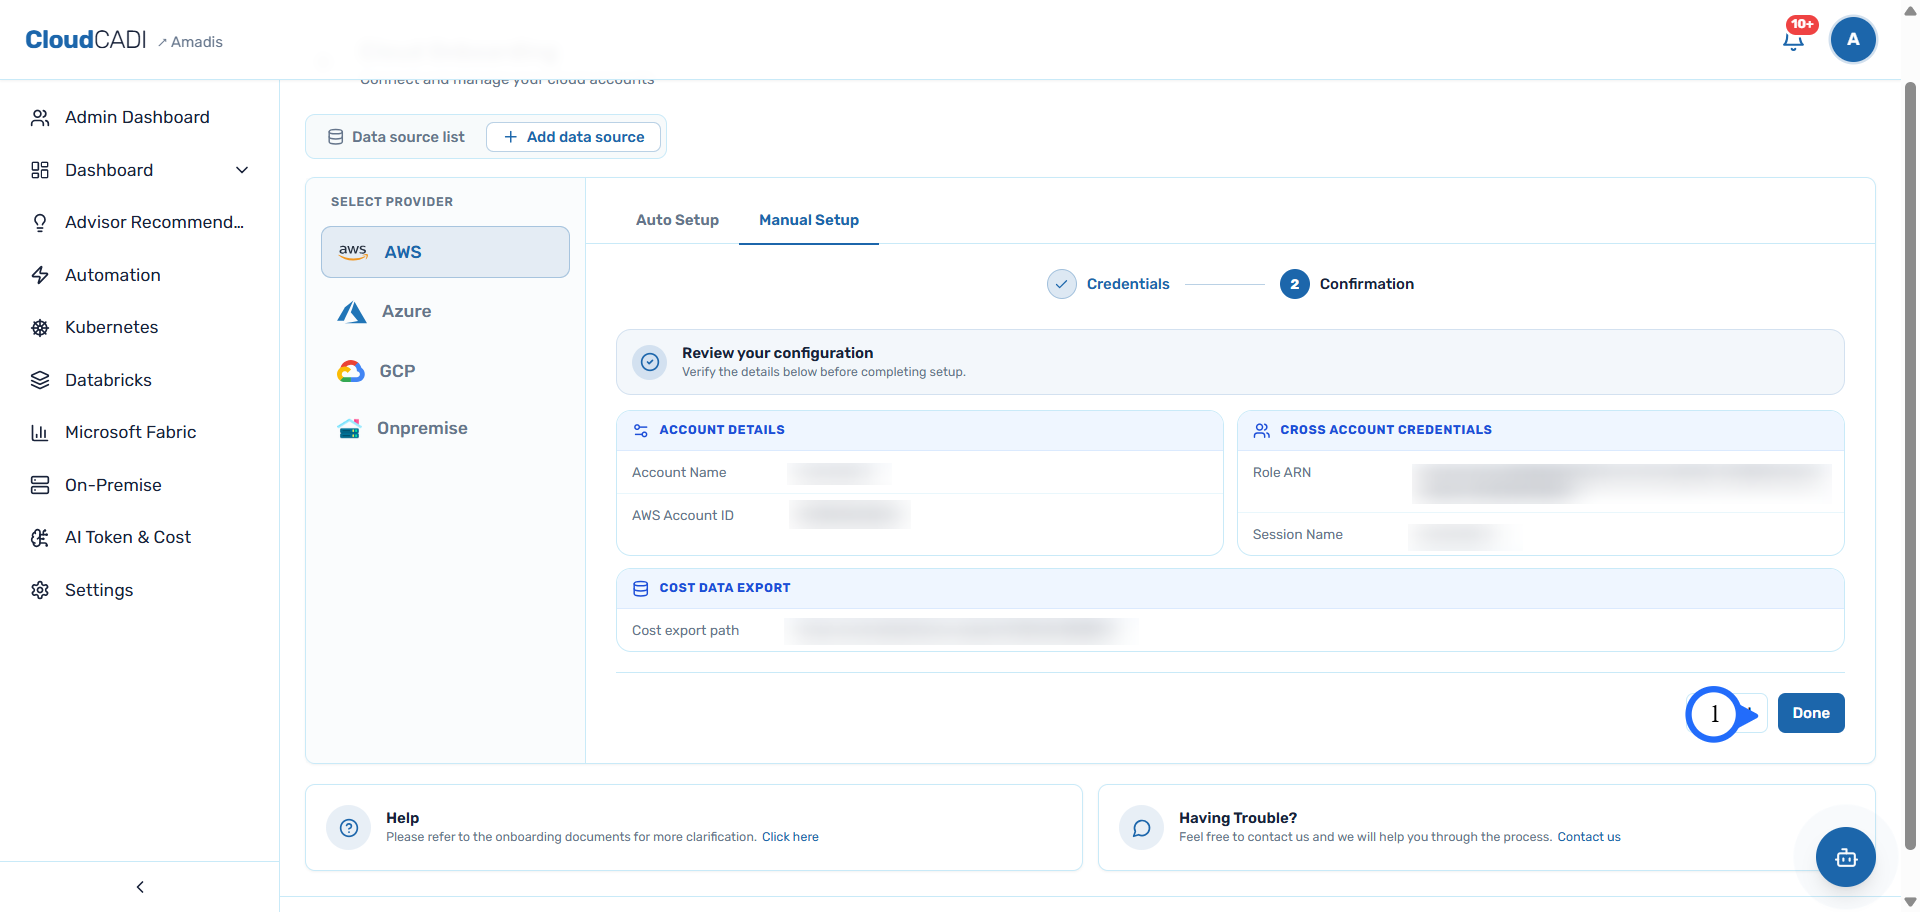
Review the configuration on the confirmation page and click Done.
Step 4 - Verify Data Source Creation
-
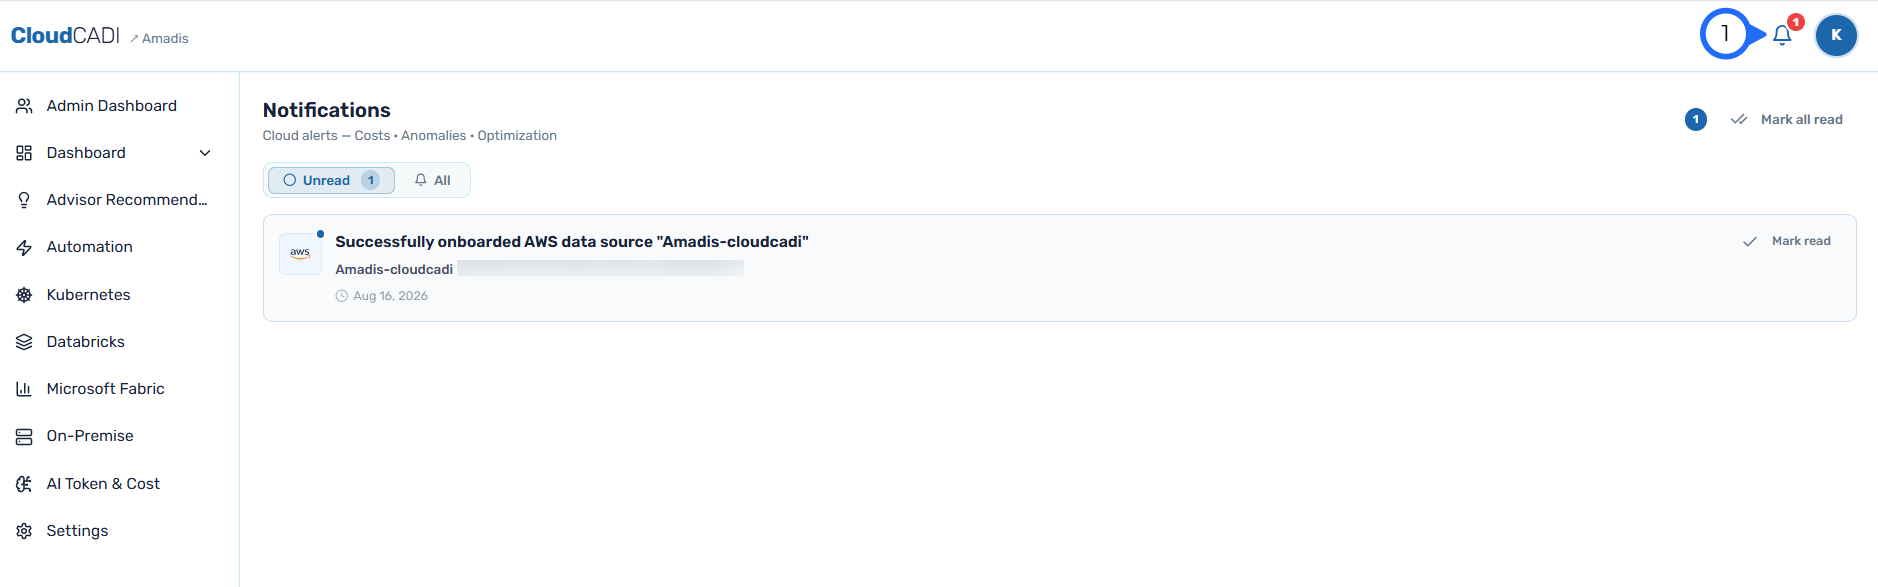
You will be redirected to the Data Sources list page. You will be notified once the accounts are onboarded.
-
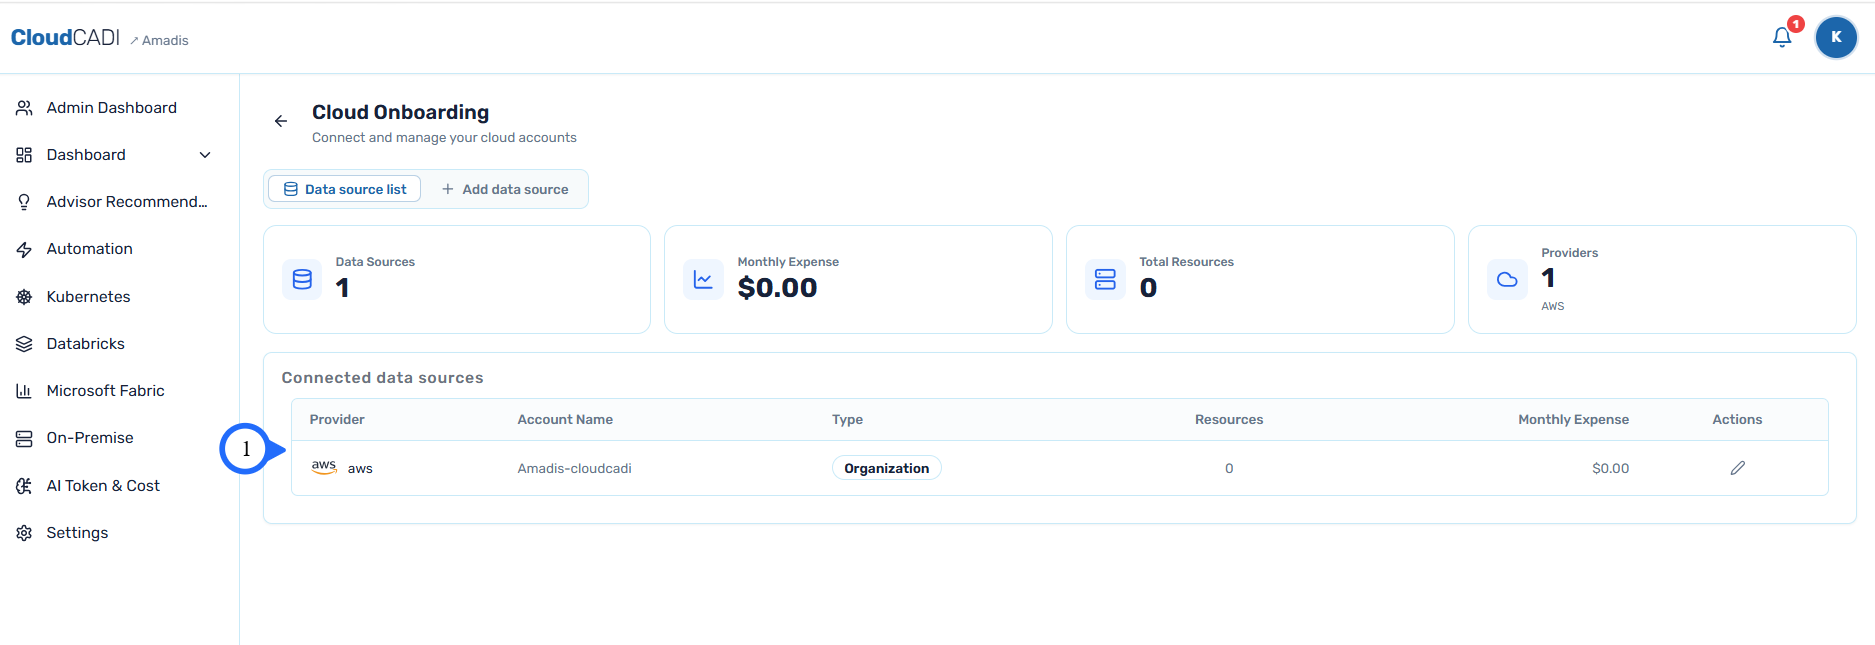
Navigate back to the Data Sources list tab and confirm the AWS account appears, with the provider shown as AWS and the configured Account name.